Bridging the Regulatory Gap
27 October 2026 | Maison de la Poste | Brussels, Belgium
A full day focused on the regulations that impact open source, including the Cyber Resilience Act and the AI Act.
ABOUT THE EVENT
Join us in Brussels
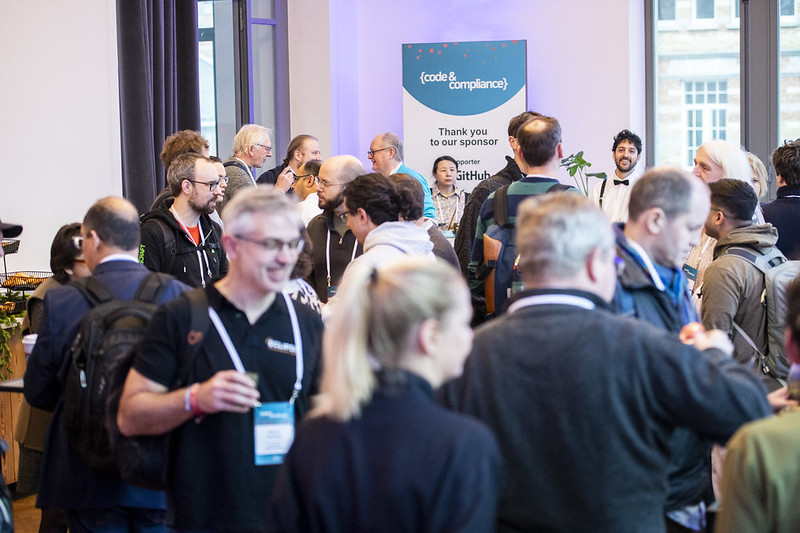
Building trust is the foundation of a resilient digital future. Code & Compliance brings industry leaders and the open source community together to close the knowledge gaps around compliance for open source software.
Across four blocks we move from policy objectives to practical implementation: securing products under the CRA, integrating open source AI models under the AI Act, and scaling shared responsibility for open source security across industry.
The day is hosted by the Open Regulatory Compliance Working Group. Sessions are practical, the room is small enough to talk in, and the outputs feed back into resources for the open source community.
WHY ATTEND
The CRA and the AI Act are here. Are you ready?
The first Cyber Resilience Act obligations have started and more arrive in 2027; and the AI Act is reshaping how open source models are built and deployed. Code & Compliance is built for the people who want to prioritise compliance without slowing down innovation.
Put regulation into practice
Practical guidance on implementing the Cyber Resilience Act, the AI Act and other evolving European requirements — aligning engineering, legal and security teams.
Meet the people shaping compliance
Regulators, industry leaders, open source maintainers and compliance experts, in one room, working out what good practice looks like.
Decode digital sovereignty
Understand how open source and open standards support European digital sovereignty and autonomy in practice.
Reduce product compliance risk
Due diligence for open source integration, SBOMs and VEX, secure-by-design playbooks, and the obligations of open source stewards under the CRA.
Built for cross-functional teams
Manufacturers and product teams, OSPOs, industry associations, policy stakeholders, and security and legal professionals.
Influence what comes next
Collaborative sessions feed directly into ORC working group guidance and future open source compliance efforts.
PROGRAMME
Four topics, one day
The programme is being finalised. Sessions and speakers may still change.
BLOCK 1 · 09:00–10:30
Shaping the digital compliance landscape
Policymakers and industry leaders bridge the gap between high-level regulatory objectives and the operational realities of the European digital landscape — cybersecurity, AI and technological sovereignty.
09:50
Navigating the regulatory landscape: From policy objectives to practical implementation
Moderator: Juan Rico, ORC
Panelists:
BLOCK 2 · 10:50–12:40
Securing products and demonstrating compliance in the times of the CRA
Beyond theory, into the how-to of compliance: due diligence in open source integration, the practical implementation of SBOMs and VEX, and blueprints for secure-by-design development.
The CRA: Status, next steps and how to support the implementation process
11:10
Due diligence obligations for the integration of open source components
Gergely Csatari, Nokia
12:10
SBOMs and its real impact on the industry
Moderator: Juan Rico, ORC
Panelists:
BLOCK 3 · 14:00–15:45
AI Act: safe integration of open source models
A clear path to compliant, responsible AI deployment — the role of open source models in the new environment, secure agentic AI, and federated security.
Moderator: Rachel Foucard
Panelists:
Block 4 · 16:15–17:35
Simplifying compliance for industrial scale
Scaling security through shared responsibility: who owns open source security, how accountability is distributed, and how compliance becomes a catalyst for innovation rather than a burden.
Physical machinery documentation turned into compliance assets – Enduradocs case
Transparency Upstream, Evidence Downstream: Manufacturers and Open Source Under the CRA
Shared responsibility: Who owns open source security?
Moderator: Marta Garcia
Panelists:
SPEAKERS
Who you will hear from
Regulators, maintainers and industry practitioners.
Public Policy Director for EMEA and APAC, Red Hat
Legal and Policy Officer, Coordinator – AI Office, European Commission (DG CONNECT)
Cybersecurity Officer, European Union Agency for Cybersecurity (ENISA)
Expert Cybersecurity Regulation and Standardisation, Agoria
Director of Product Security Regulations & Standards, Arm
CIO, Board Member, Kombud Group S.A.
Legal Counsel Security, Knorr-Bremse
Policy Officer, ICT Standardisation, European Commission (DG CONNECT)