ABOUT THE EVENT
Regulation during Open Source Week
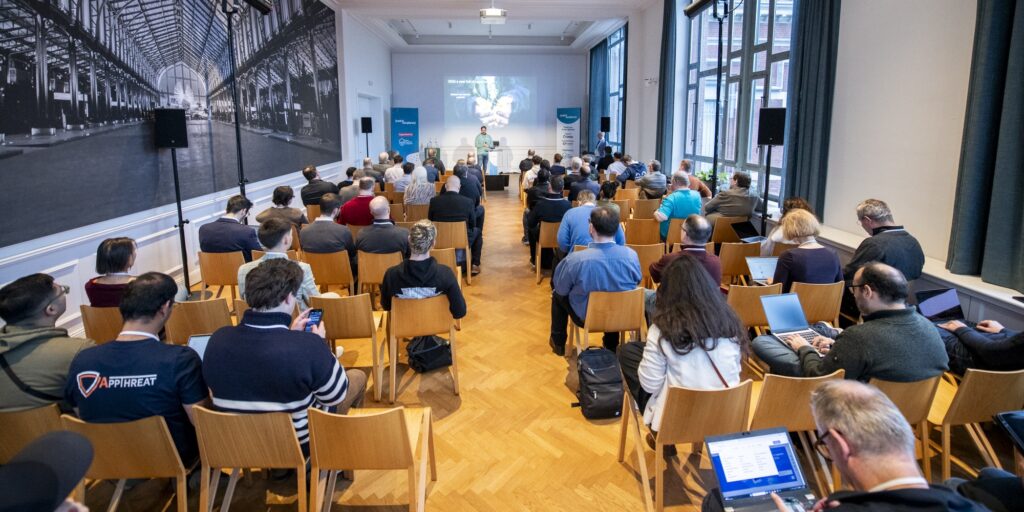
Code & Compliance returns to Brussels the week of FOSDEM, and this edition is aimed squarely at maintainers and engineers. Expect implementation detail, working examples and open discussion.
The Open Regulatory Compliance Working Group has grown beyond the Cyber Resilience Act: sessions will cover the AI Act alongside the CRA, and how both impact the projects and products people actually ship.
Sessions are practical, the room is small enough to talk in, and the outputs feed back into resources for the open source community.
CALL FOR PROPOSALS
Share your work, start the conversation
We are looking for talks exploring the Cyber Resilience Act (CRA) and EU AI Act, with a particular focus on a challenge at the heart of ORC’s work: bridging the gap between regulatory obligations and the realities of open source development.
As manufacturers and AI providers prepare to meet new requirements, questions remain about what they can reasonably expect from the open source projects and communities they depend on. How are developers, maintainers, foundations and companies addressing these challenges together? We welcome practical experiences with vulnerability management, SBOMs, security attestations, technical and model documentation, due diligence, and new approaches to shared responsibility. Case studies, open source tools, emerging solutions, unresolved challenges and lessons learned are all encouraged.
Closes 7 December 2026
TICKETS
Our most popular event of the year
Space is limited and this event is likely to sell out. Register early to secure your seat.
Standard
€120
Full-day access to all sessions.
Members
50% OFF
Discount code will be shared on the ORC mailing list.
KEY DATES
What happens when
These are the dates to watch — this page will be updated as each one arrives.
27 October 2026
Call for proposals opens
Aligned with the opening of the FOSDEM call for participation.
27 October 2026
Registration opens
This is our most popular event of the year, space is limited.
7 December 2026
Call for proposals closes
Note: Date subject to change.
28 January 2027
Code & Compliance | FOSDEM Edition
Maison de la Poste, Brussels, Belgium.
WHY ATTEND
The CRA and the AI Act are here. Are you ready?
The first Cyber Resilience Act obligations have started and more arrive in 2027; and the AI Act is reshaping how open source models are built and deployed. Code & Compliance is built for the people who want to prioritise compliance without slowing down innovation.
Put regulation into practice
Practical guidance on implementing the Cyber Resilience Act, the AI Act and other evolving European requirements — aligning engineering, legal and security teams.
Meet the people shaping compliance
Regulators, industry leaders, open source maintainers and compliance experts, in one room, working out what good practice looks like.
Decode digital sovereignty
Understand how open source and open standards support European digital sovereignty and autonomy in practice.
Reduce product compliance risk
Due diligence for open source integration, SBOMs and VEX, secure-by-design playbooks, and the obligations of open source stewards under the CRA.
Built for cross-functional teams
Manufacturers and product teams, OSPOs, industry associations, policy stakeholders, and security and legal professionals.
Influence what comes next
Collaborative sessions feed directly into ORC working group guidance and future open source compliance efforts.
PROGRAMME
Four topics, one day
The programme is being finalised. Sessions and speakers may still change.
BLOCK 1 · 09:00–10:30
Shaping the digital compliance landscape
Policymakers and industry leaders bridge the gap between high-level regulatory objectives and the operational realities of the European digital landscape — cybersecurity, AI and technological sovereignty.
09:00
Welcome to Code & Compliance
Gaël Blondelle, Eclipse Foundation
09:10
Keynote
TBC
09:50
Navigating the Regulatory Landscape: From Policy Objectives to Practical Implementation
Panel Discussion
BLOCK 2 · 10:50–12:40
Securing products and demonstrating compliance in the times of the CRA
Beyond theory, into the how-to of compliance: due diligence in open source integration, the practical implementation of SBOMs and VEX, and blueprints for secure-by-design development.
The CRA: Status, next steps and how to support the implementation process
Tommaso
11:10
Due diligence obligations for the integration of open source components
Timo Perälä
11:30
TBC
TBC
11:50
Secure by design and default playbook + intro to SBOMs + VEX
ENISA Representative (TBC)
12:10
SBOMs and its real impact on the industry
Panel Discussion
BLOCK 3 · 14:00–15:45
AI Act: safe integration of open source models
A clear path to compliant, responsible AI deployment — the role of open source models in the new environment, secure agentic AI, and federated security.
Programme still under development
TBD
Block 4 · 16:15–17:35
Simplifying compliance for industrial scale
Scaling security through shared responsibility: who owns open source security, how accountability is distributed, and how compliance becomes a catalyst for innovation rather than a burden.
Programme still under development
TBD
SPEAKERS
Who you will hear from
Regulators, maintainers and industry practitioners.
Founder, Null Point Studio
VP of Public Affairs, The Apache Software Foundation (ASF)
Principal Compliance Program Manager, Red Hat
Owner & CEO, Edvina.net
Senior Program Manager, Red Hat
CEO | Principal Software Architect, EclipseSource
Head of Open Source Service & Network Automation, Nokia